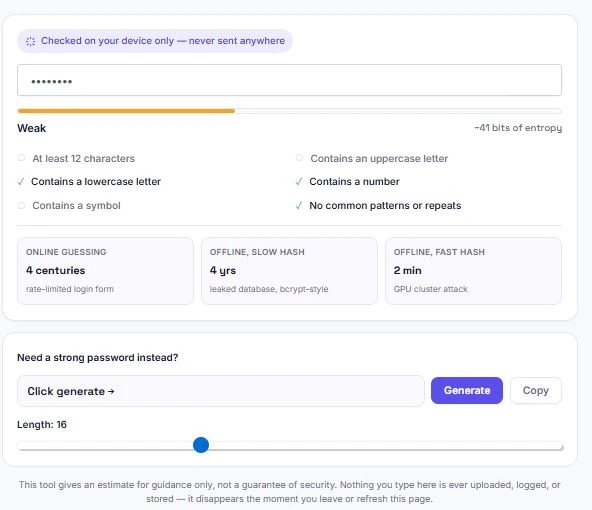
A password strength checker analyzes a password in real time and estimates how hard it would actually be for an attacker to guess — measured in entropy (bits) rather than just counting characters. This free password strength checker runs entirely in your browser: as you type, it checks length, character variety, and whether the password matches a known weak pattern, such as a common password, a keyboard sequence like "qwerty," or a repeated character.
It also estimates realistic crack times across three attack scenarios — a rate-limited login form, an offline slow-hash database leak, and a GPU-powered offline attack — so the result reflects how a password would hold up in the real world, not just a generic score. Nothing you type is uploaded, logged, or stored; the check happens entirely on your device and disappears the moment you leave the page.
Click generate →
This tool gives an estimate for guidance only, not a guarantee of security. Nothing you type here is ever uploaded, logged, or stored — it disappears the moment you leave or refresh this page.
How This Password Strength Checker Works
Most simple password checkers just count how many character types you used and call a long password "strong" — even if it's something predictable like "aaaaaaaaaaaa" repeated twelve times. This checker works differently. It first calculates raw entropy, the theoretical number of guesses an attacker would need based on your password's length and character pool.
Then it actively scans for weaknesses that reduce real-world security: whether the password appears on a list of commonly breached passwords, whether it contains a keyboard pattern like "asdfgh," and whether it has repeated or sequential characters like "1234" or "xyz." When a pattern is detected, the score is adjusted down to reflect how quickly an attacker who already knows these tricks could crack it — not just how it looks on paper.
What Makes a Password Weak
A password can look complex and still be weak if it follows a pattern an attacker's software already knows to try first. These are the most common weaknesses this checker looks for:
- Common passwords — words like "password," "welcome," or "letmein" that appear on every breach list and get tried within the first few seconds of an attack.
- Keyboard patterns — sequences like "qwerty," "asdfgh," or "zxcvbn" that follow the physical layout of a keyboard rather than being random.
- Sequential characters — runs like "1234," "abcd," or "9876" that are trivial to guess once a pattern is spotted.
- Repeated characters — strings like "aaaa" or "1111" that add length without adding real unpredictability.
- Personal information — names, birthdates, or usernames, which attackers often already have access to when targeting a specific account.
- Short length — anything under 12 characters, since shorter passwords have far fewer possible combinations regardless of complexity.
Password Strength Levels Explained
This checker scores every password on a five-level scale based on adjusted entropy — the effective number of bits left after weak patterns are accounted for. Here's what each level means in practice:
| Level | Entropy (bits) | What It Means |
|---|---|---|
| Very Weak | Below 30 bits | Crackable almost instantly, often a common password or short/simple pattern |
| Weak | 30–44 bits | Falls to an offline attack within minutes to hours |
| Fair | 45–64 bits | Reasonable for low-risk accounts, but not strong enough for email or banking |
| Strong | 65–89 bits | Resistant to offline attacks using current consumer hardware |
| Very Strong | 90+ bits | Effectively uncrackable with any practical attack today |
How Long Would It Take to Crack Your Password?
Crack time depends entirely on how an attacker is trying to guess your password, which is why this checker shows three scenarios instead of one generic number. An online attack against a rate-limited login form is slow, often capped around 100 guesses per second. An offline attack against a leaked database using a slow, deliberately-designed hash function is faster. The worst case is an offline attack using GPU hardware against a fast, poorly-secured hash — capable of roughly 10 billion guesses per second. The gap between these numbers is enormous, which is exactly why security researchers no longer treat "crack time" as a single fixed answer.
| Attack Scenario | Guess Rate | Example: 8-Character Common Word |
|---|---|---|
| Online, rate-limited login | ~100 guesses/sec | A few minutes to hours |
| Offline, slow hash (leaked database) | ~10,000 guesses/sec | A few seconds |
| Offline, fast hash (GPU cluster) | ~10 billion guesses/sec | Instantly |
FAQs
Is this password strength checker really free?
Yes. There's no account, no sign-up, and no limit on how many passwords you can check.
Is my password uploaded or stored anywhere?
No. The entire check runs in your browser using JavaScript. Nothing you type is sent to a server, logged, or saved — closing or refreshing the page clears it completely.
What does "entropy" mean in the results?
Entropy, measured in bits, represents how many attempts an attacker would realistically need to guess your password. Higher bits mean a stronger, less predictable password.
Quick Summary
This free password strength checker analyzes your password in real time using entropy calculation, not just character count. It detects common passwords, keyboard patterns, and repeated characters, then estimates realistic crack times across three attack scenarios. Nothing you type is ever uploaded or stored — everything happens in your browser.
Disclaimer
BytePriva's Password Strength Checker is a free browser-based tool provided for general guidance. All analysis happens locally in your browser — no password is ever uploaded, transmitted, or stored. This tool does not check against real-time data breach databases and does not guarantee that a password rated "Strong" or "Very Strong" is immune to all forms of attack. Password security also depends on factors outside this tool's scope, such as two-factor authentication and how a service stores its passwords. Use of this tool is at your own discretion.